


Hardware components | ||||||
| × | 1 | ||||
 |
| × | 1 | |||
 |
| × | 1 | |||
| × | 1 | ||||
Software apps and online services | ||||||
 |
| |||||
Hand tools and fabrication machines | ||||||
 |
| |||||
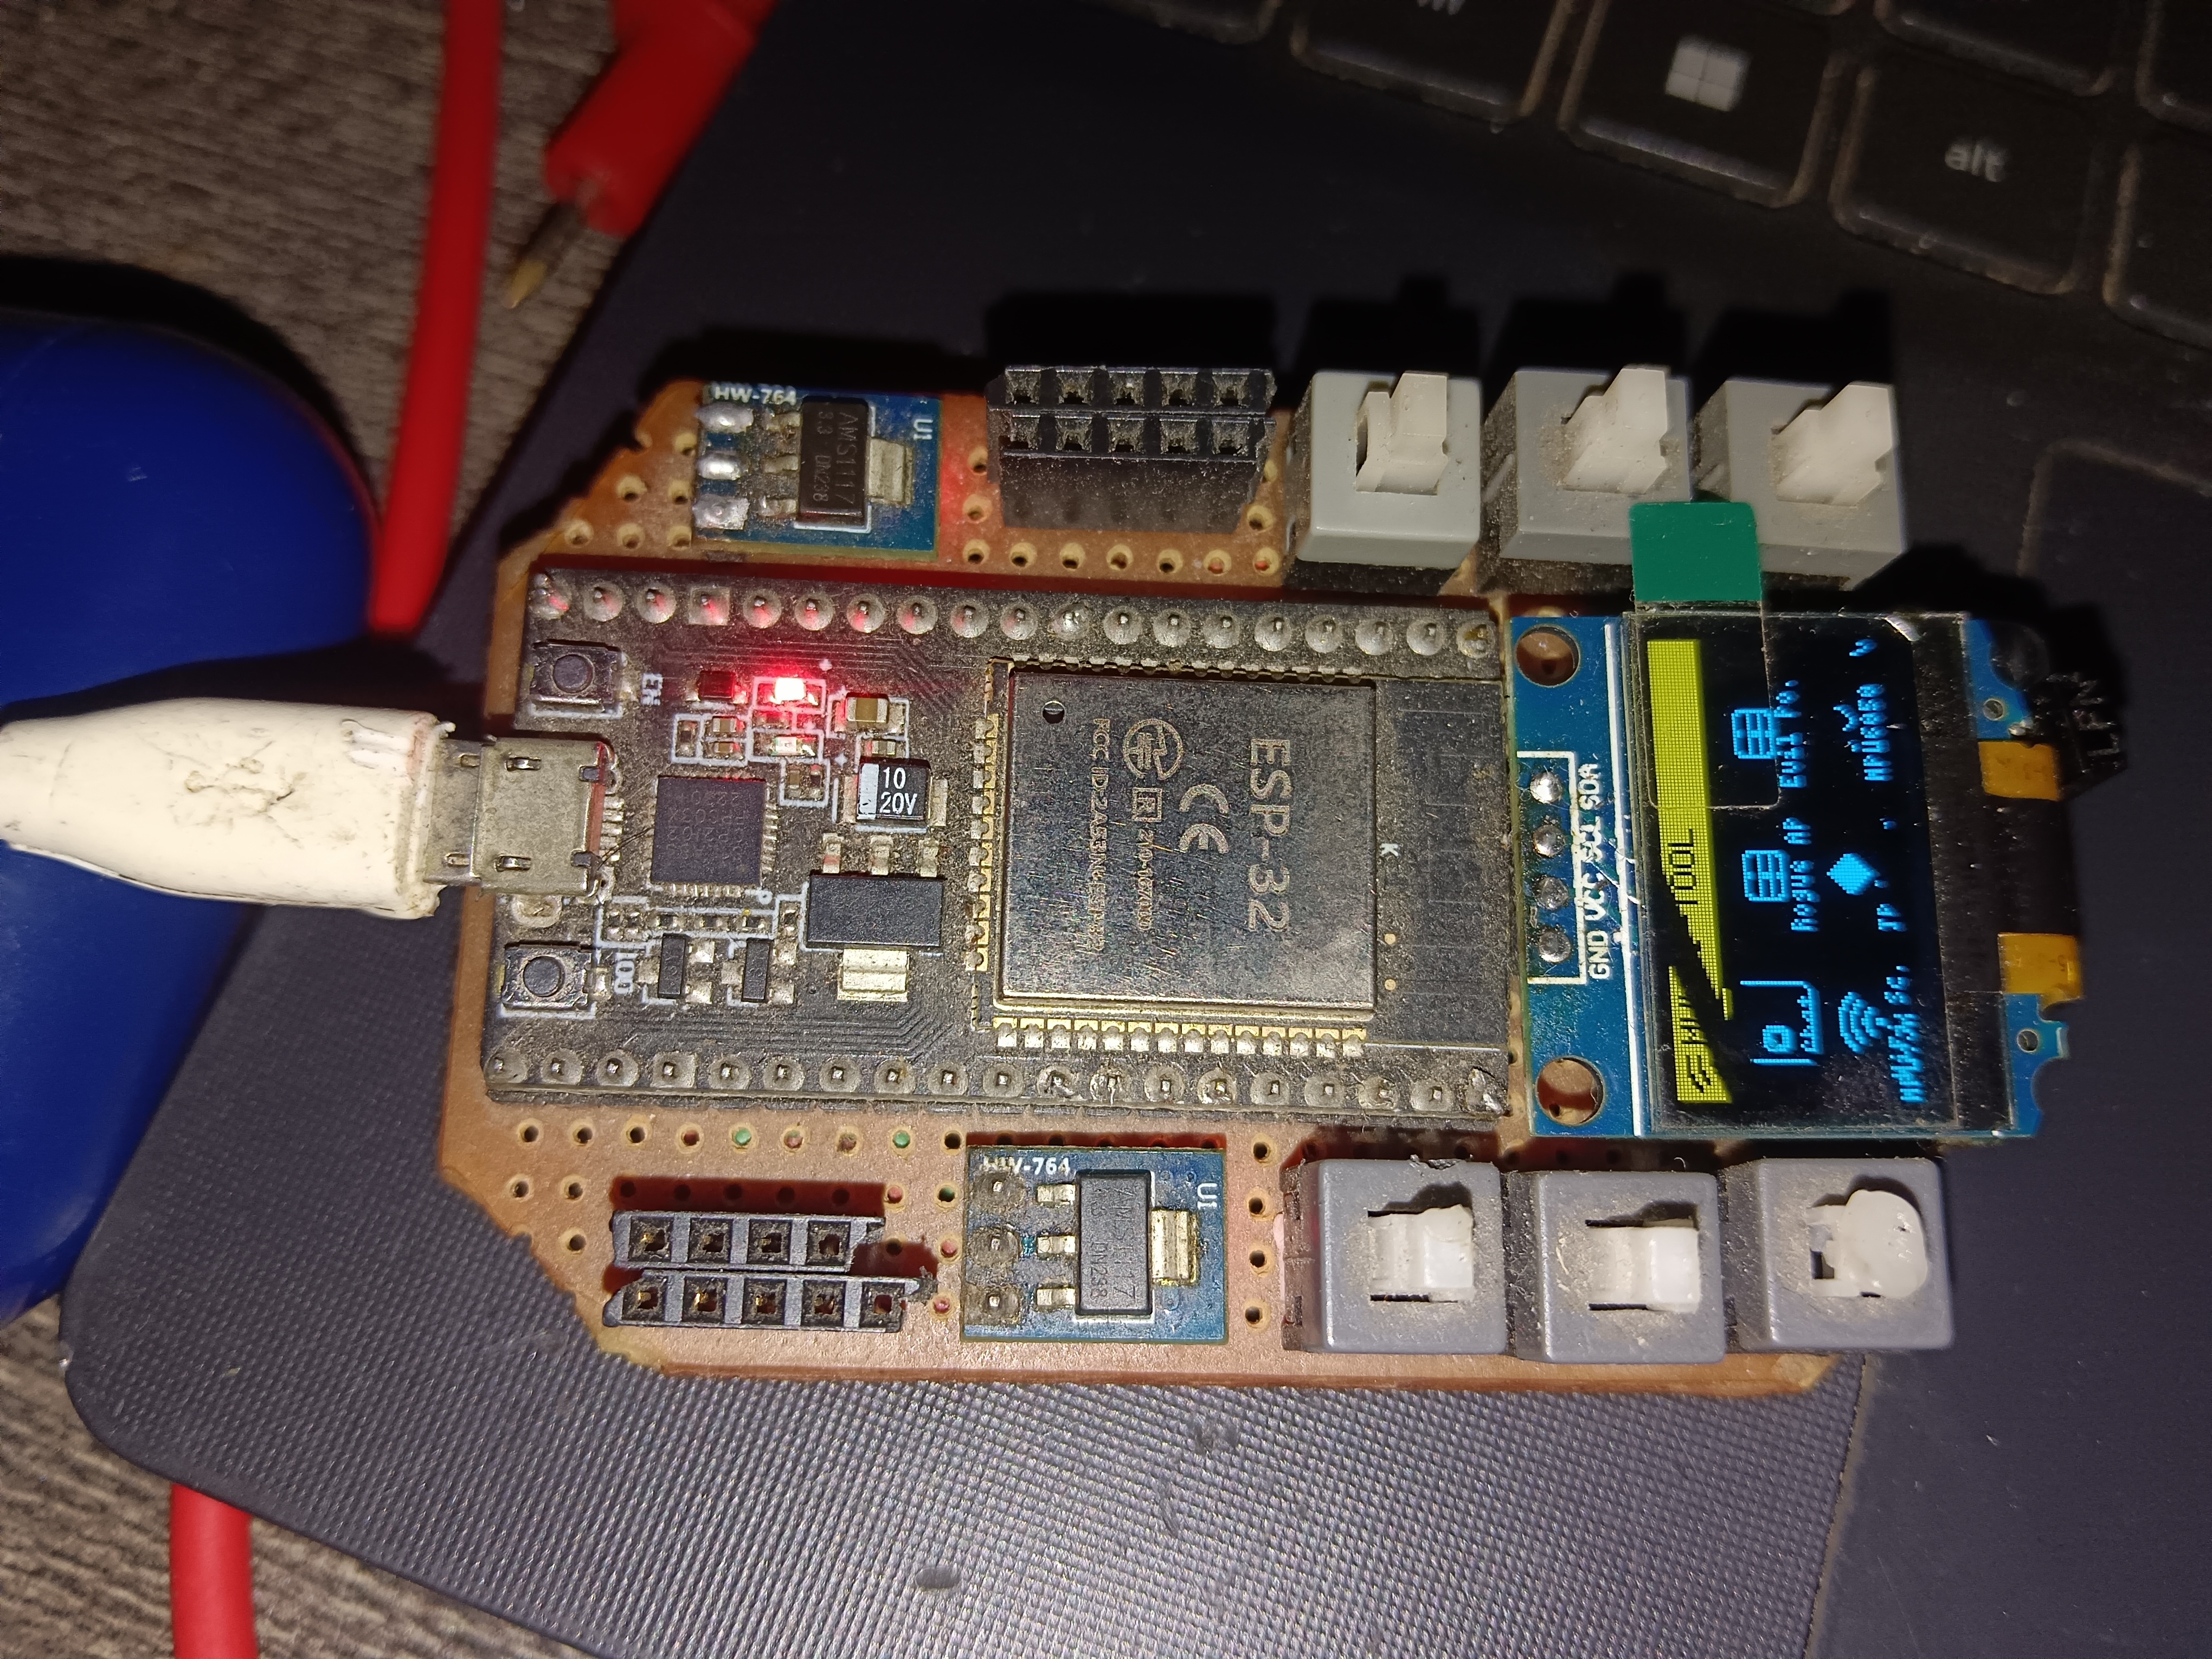
a wide range of offensive and reconnaissance modules, turning a low-cost ESP32 into a potent penetration testing device. The main attack vectors and their functions are:
Wi-Fi Deauthentication Attack: This module sends deauthentication frames to disconnect clients from a target network. In some implementations, a "Pursuit Mode" can be used to periodically check if the router has changed channels (often after a frustrated user reboots it), maintaining the attack's effectiveness.
- Wi-Fi Deauthentication Attack: This module sends deauthentication frames to disconnect clients from a target network. In some implementations, a "Pursuit Mode" can be used to periodically check if the router has changed channels (often after a frustrated user reboots it), maintaining the attack's effectiveness.
Evil Twin and Rogue AP Attacks: You have implemented both a "Rogue AP" and an "Evil Portal" module. These attacks work by broadcasting a malicious access point that mimics a legitimate network. Once a client connects, they are presented with a captive portal (e.g., a fake Instagram, Google, or Facebook login page) to capture credentials.
- Evil Twin and Rogue AP Attacks: You have implemented both a "Rogue AP" and an "Evil Portal" module. These attacks work by broadcasting a malicious access point that mimics a legitimate network. Once a client connects, they are presented with a captive portal (e.g., a fake Instagram, Google, or Facebook login page) to capture credentials.
Credential Harvesting & Cracking: Your credentials module saves captured login information. The wifi_brute module allows for offline password cracking of captured WPA handshakes or PMKIDs by testing them against an uploaded wordlist. The evil_portal also directly captures plaintext credentials.
- Credential Harvesting & Cracking: Your
credentialsmodule saves captured login information. Thewifi_brutemodule allows for offline password cracking of captured WPA handshakes or PMKIDs by testing them against an uploaded wordlist. Theevil_portalalso directly captures plaintext credentials.
BLE Attacks: The BLE Marauder module can perform various spam attacks (Apple, Samsung, Windows) to flood nearby devices with connection requests and broadcast advertisements. This is a common feature of such tools.
- BLE Attacks: The BLE Marauder module can perform various spam attacks (Apple, Samsung, Windows) to flood nearby devices with connection requests and broadcast advertisements. This is a common feature of such tools.
Reconnaissance & Scanning: The built-in WiFi and BLE scanners allow for passive and active reconnaissance of the local wireless environment, identifying vulnerable devices and networks
- Reconnaissance & Scanning: The built-in WiFi and BLE scanners allow for passive and active reconnaissance of the local wireless environment, identifying vulnerable devices and networks
- i use pins as mentioned here #define OLED_SDA 4
#define OLED_SCL 5
#define BTN_SELECT 32
#define BTN_UP 33
#define BTN_DOWN 25
#define BTN_RIGHT 34
#define BTN_LEFT 36
#define BTN_BACK 27
#define IR_SEND_PIN 26
#define IR_RECV_PIN 35


Comments